AI Policy & Usage Monitor
Spot sensitive data headed to AI tools and report on policy use
A security concept that tracks AI tool usage, detects sensitive data in prompts, and alerts compliance teams under configurable policy rules.
Selected work / 01
Production operations, applied AI, innovation concepts, and the applications that started my engineering journey.
36 projects
Spot sensitive data headed to AI tools and report on policy use
A security concept that tracks AI tool usage, detects sensitive data in prompts, and alerts compliance teams under configurable policy rules.
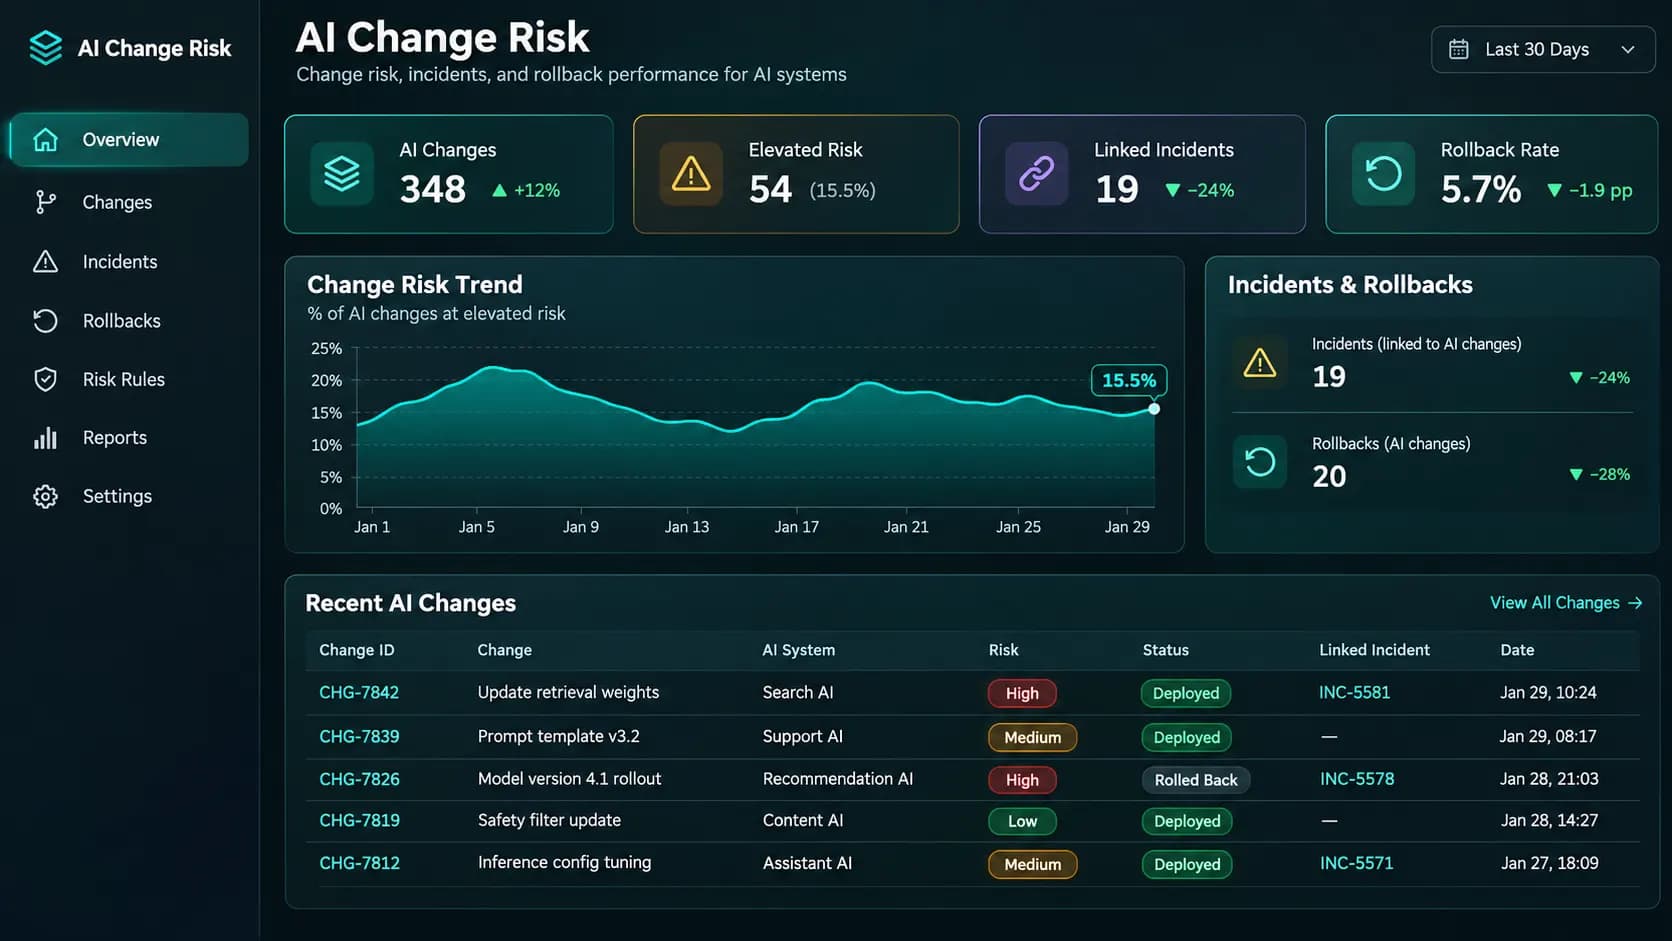
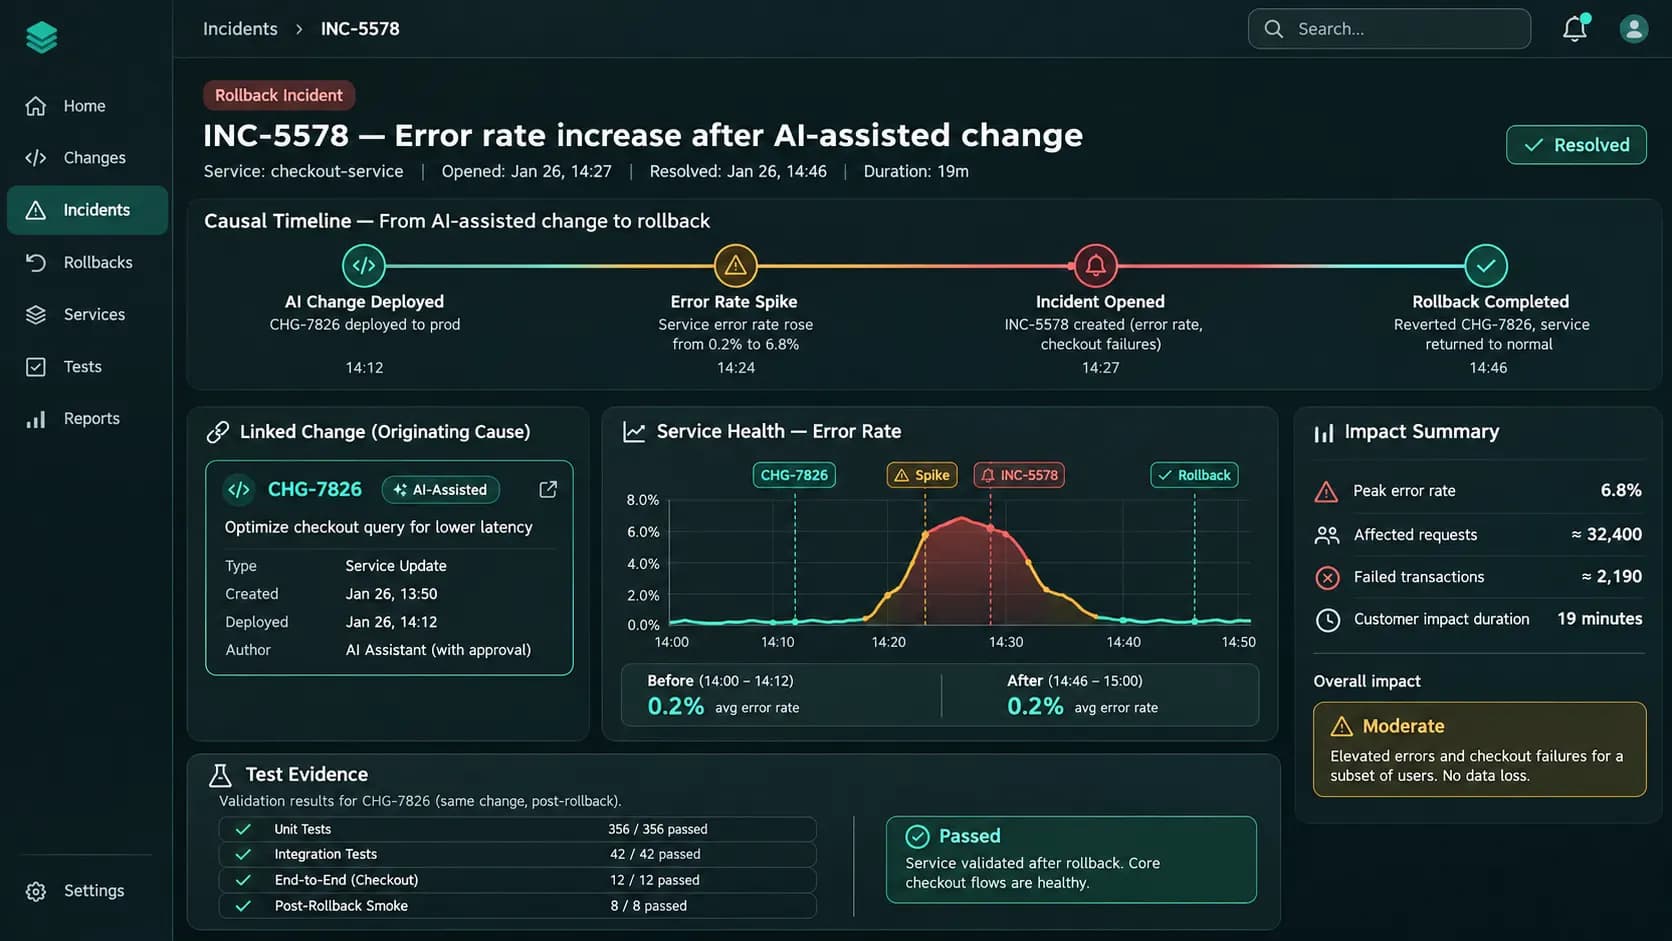
Trace AI-generated changes to tests, incidents, and rollbacks
An engineering analytics concept that attributes AI-assisted changes and connects them to test results, incidents, rollbacks, and reviewer approvals.
Draft proposals from approved pricing, case studies, and language
A retrieval concept that searches past proposals, pricing rules, and case studies to assemble approved proposal drafts with controlled language.
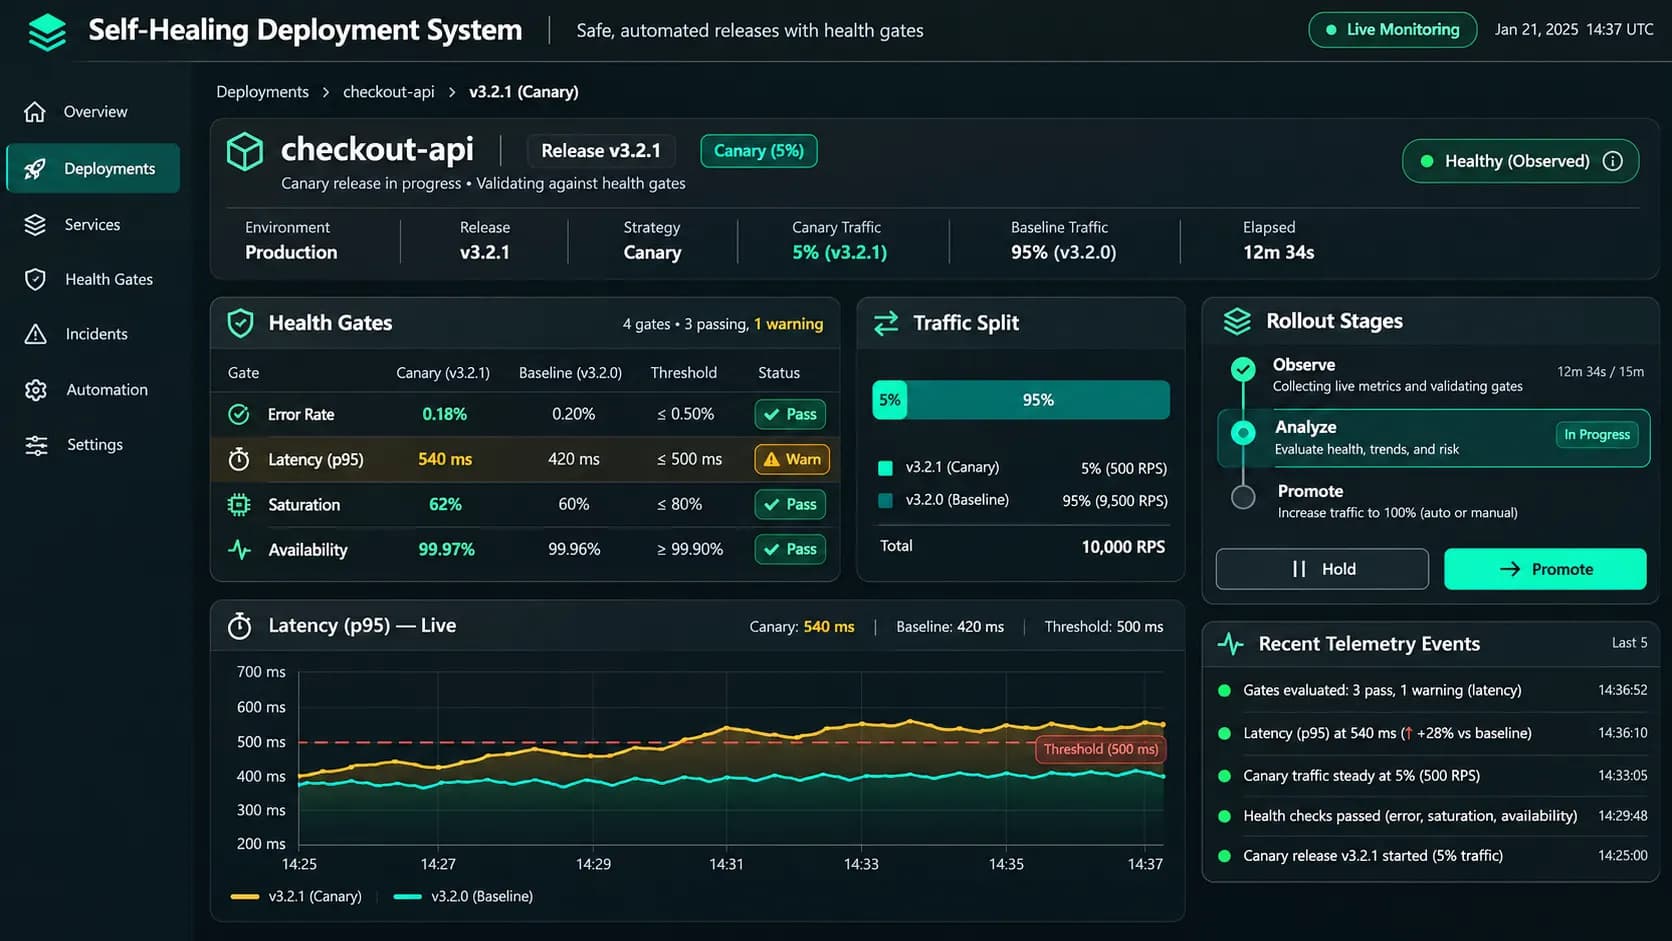
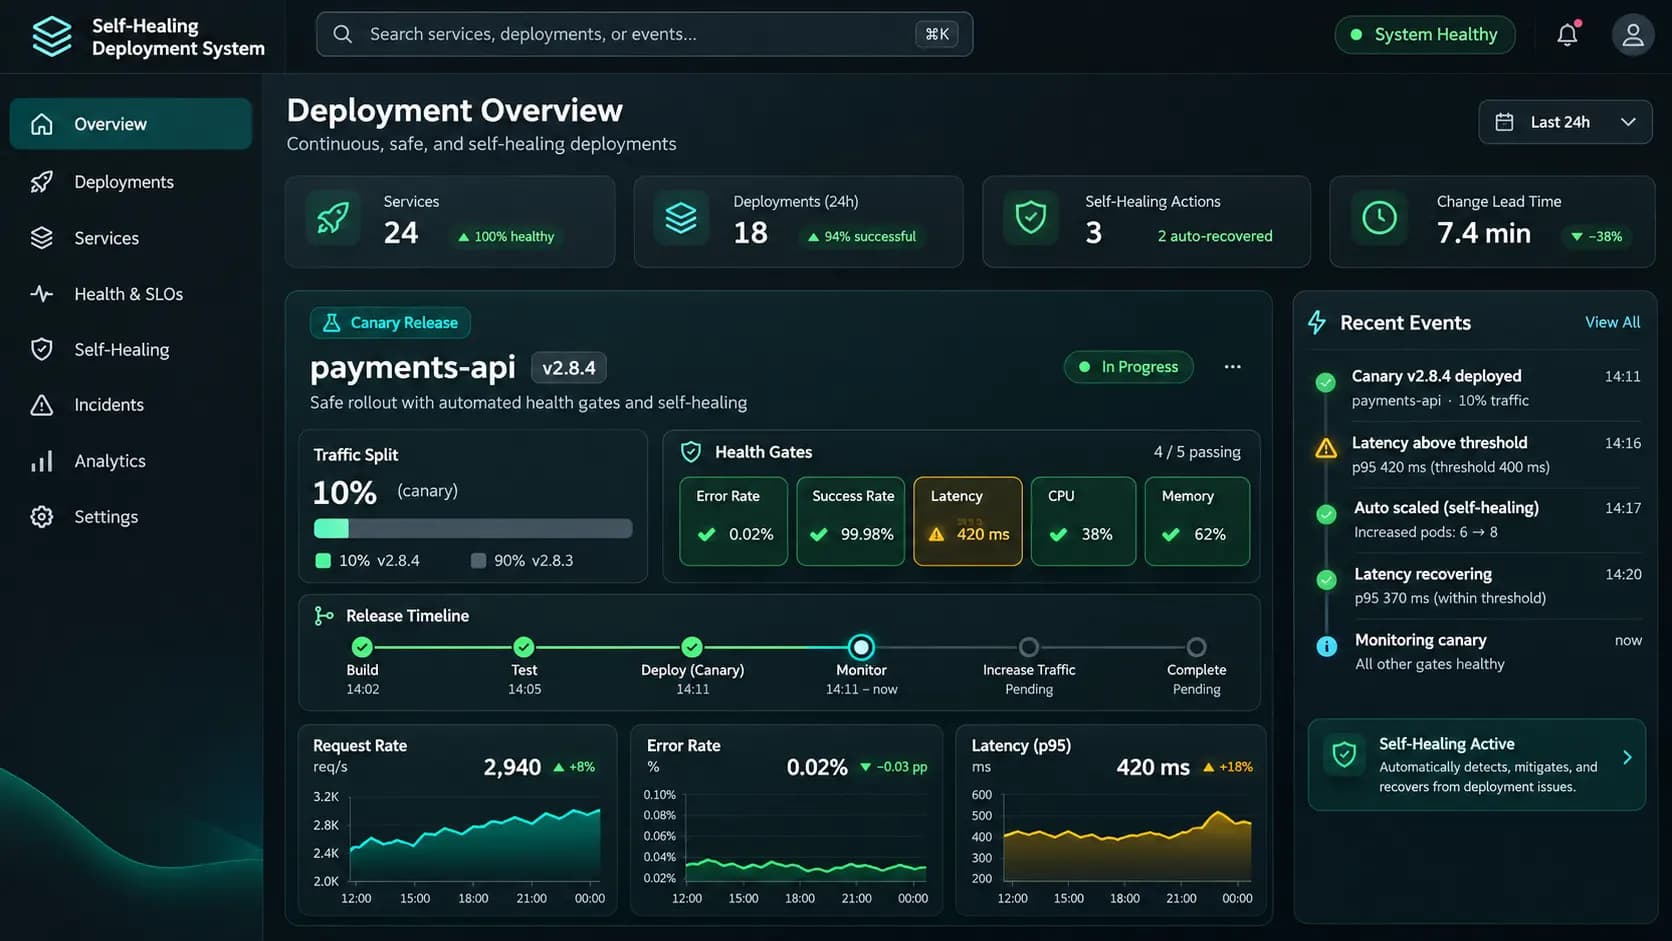
Detect a bad release, roll back, and open a diagnosed incident
A release concept that watches health checks during canary rollout, rolls back automatically on failure, captures diagnostics, and opens an incident with a likely cause.
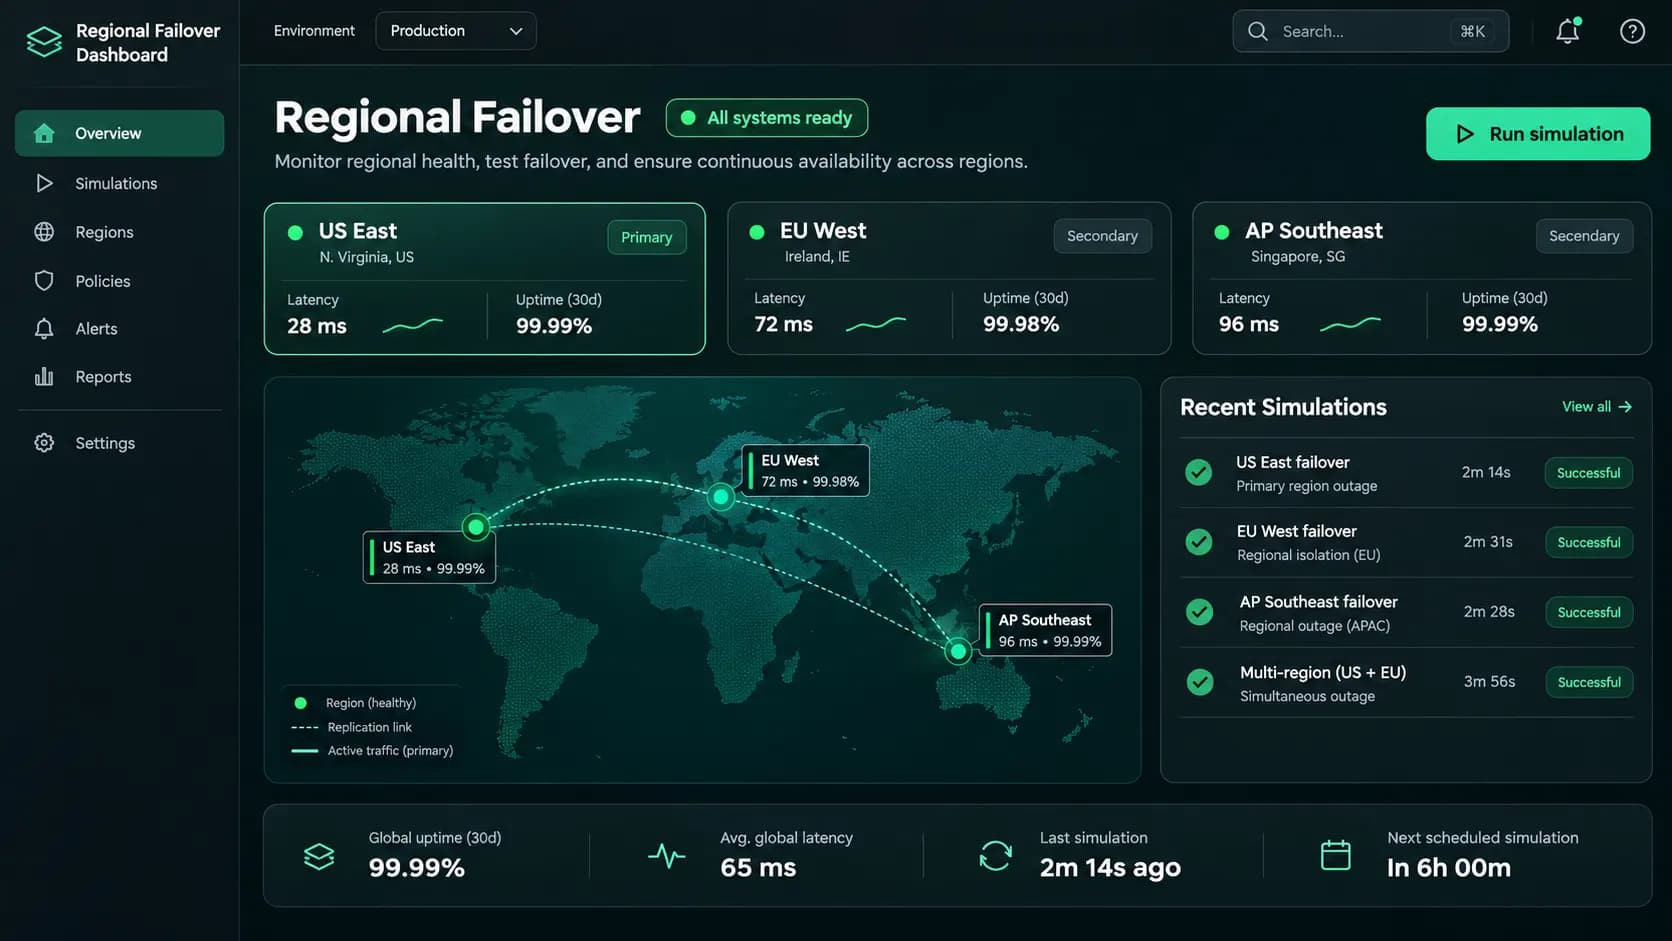
Prove a service can survive a regional outage before it happens
A reliability concept that monitors services across regions, runs failover simulations, and alerts before latency, errors, or capacity become critical.
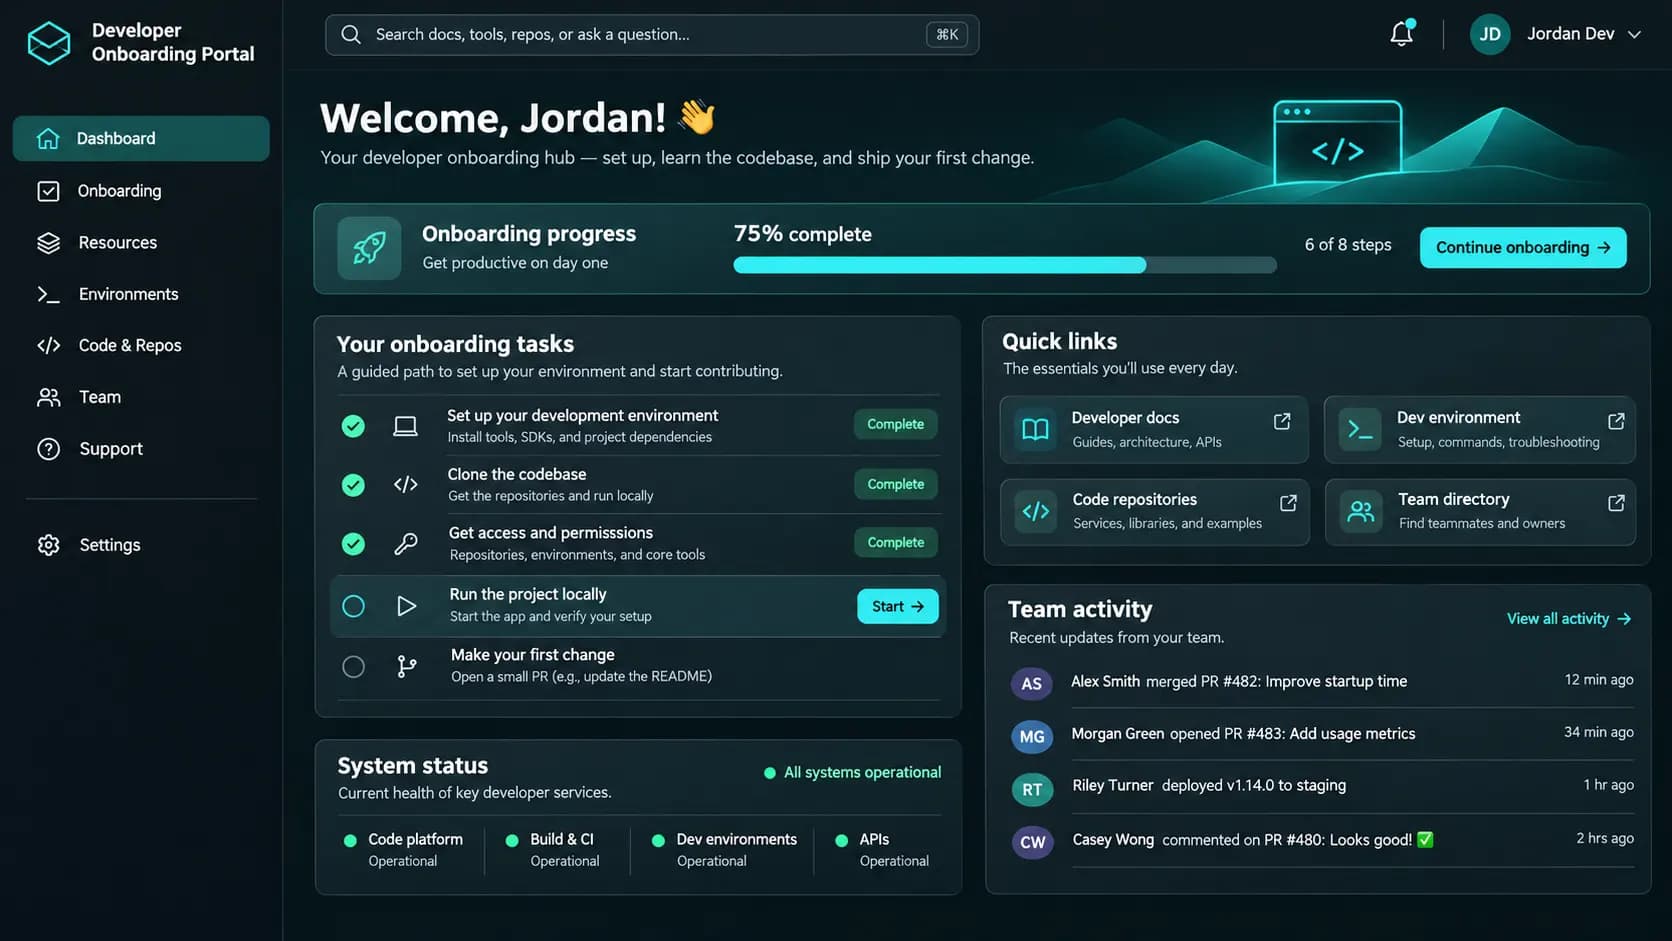
Get a new developer productive on day one
A platform concept where one portal provisions repositories, environments, seed data, credentials, and access, and tracks onboarding progress.
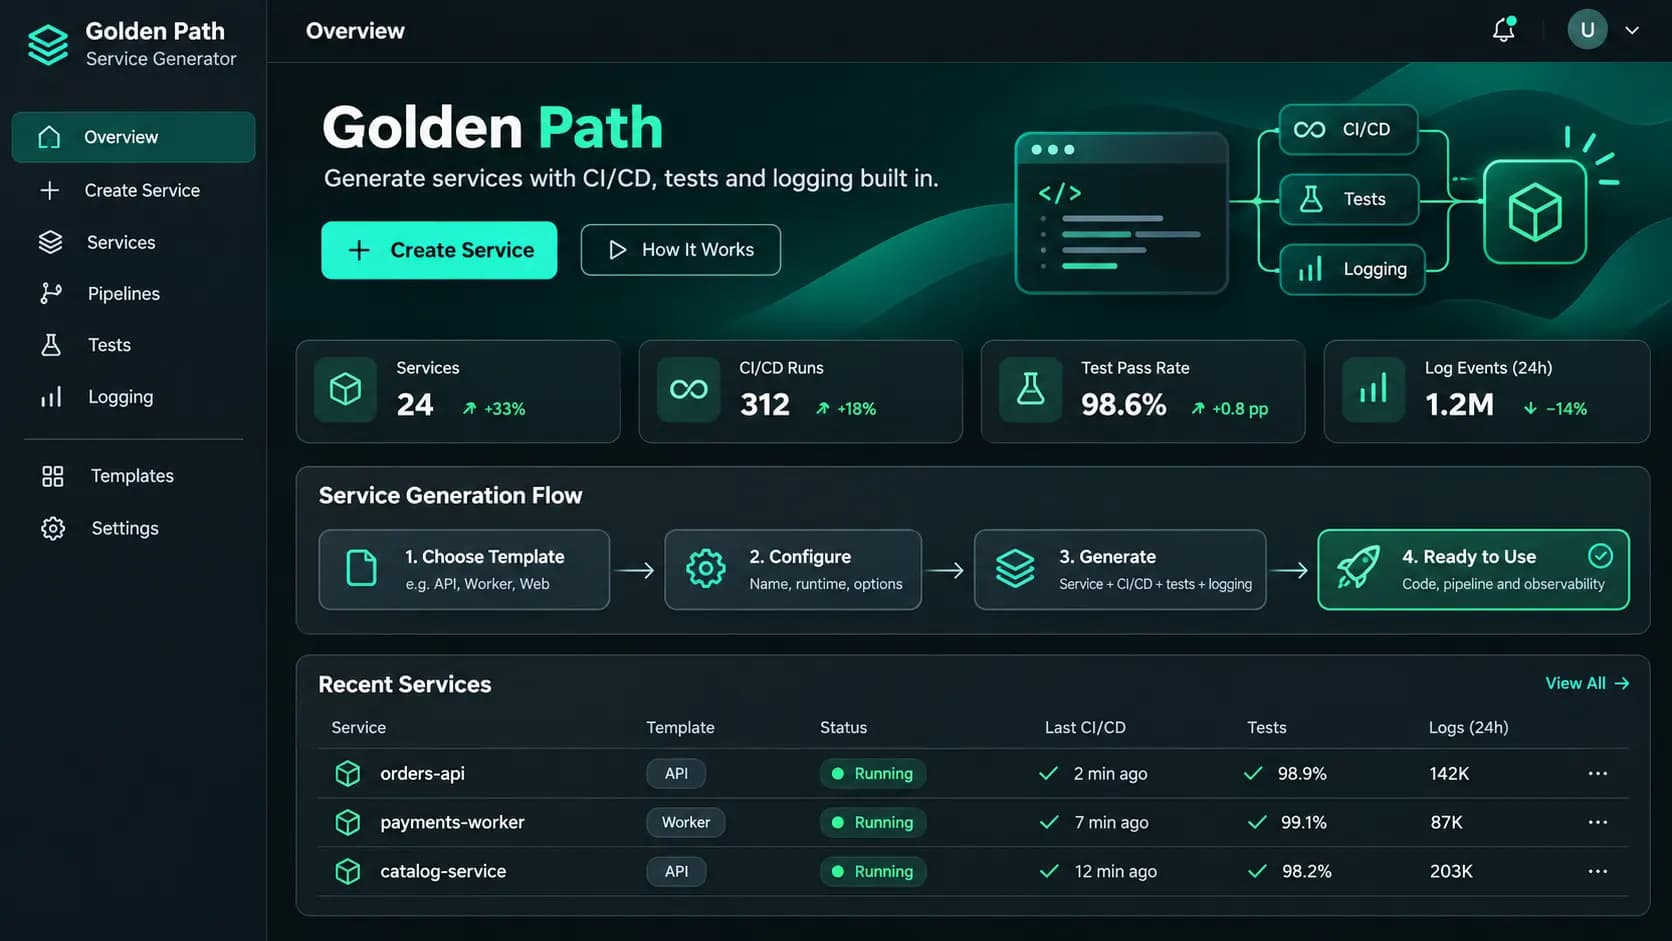
Generate a new service with CI/CD, tests, and logging built in
A platform concept for a CLI and UI that scaffolds services from approved templates including repository, CI/CD, Docker, tests, logging, and deployment.
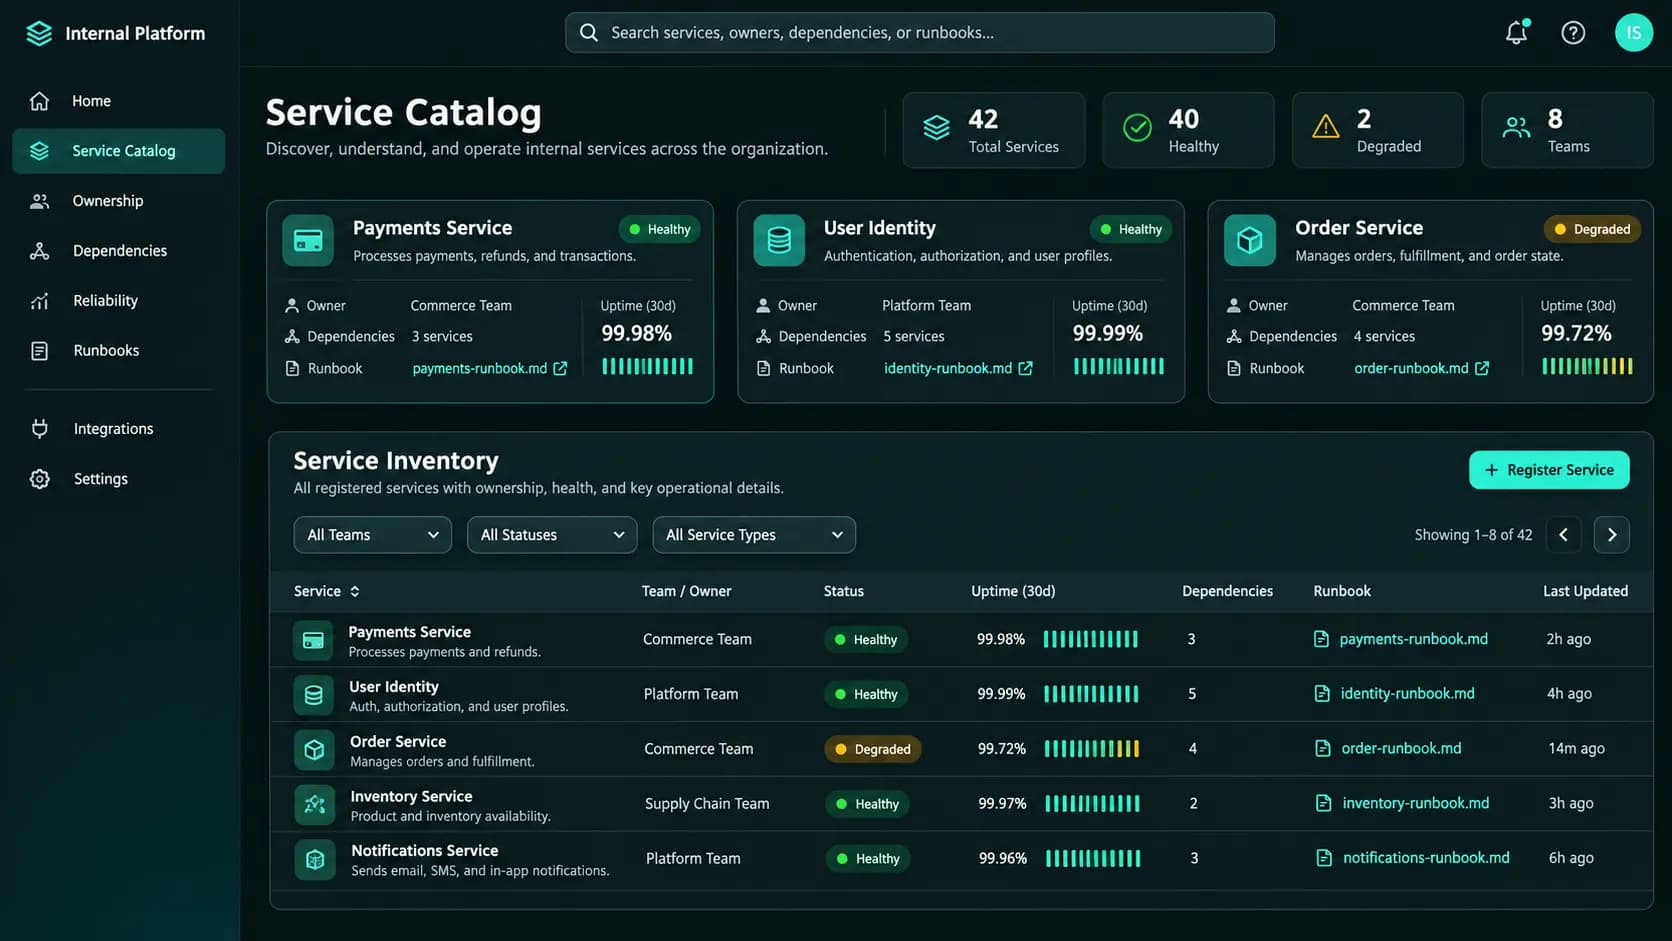
Find service owners, dependencies, and runbooks in seconds
A catalog concept showing every service with owner, dependencies, SLAs, runbooks, on-call contacts, and deployment status.
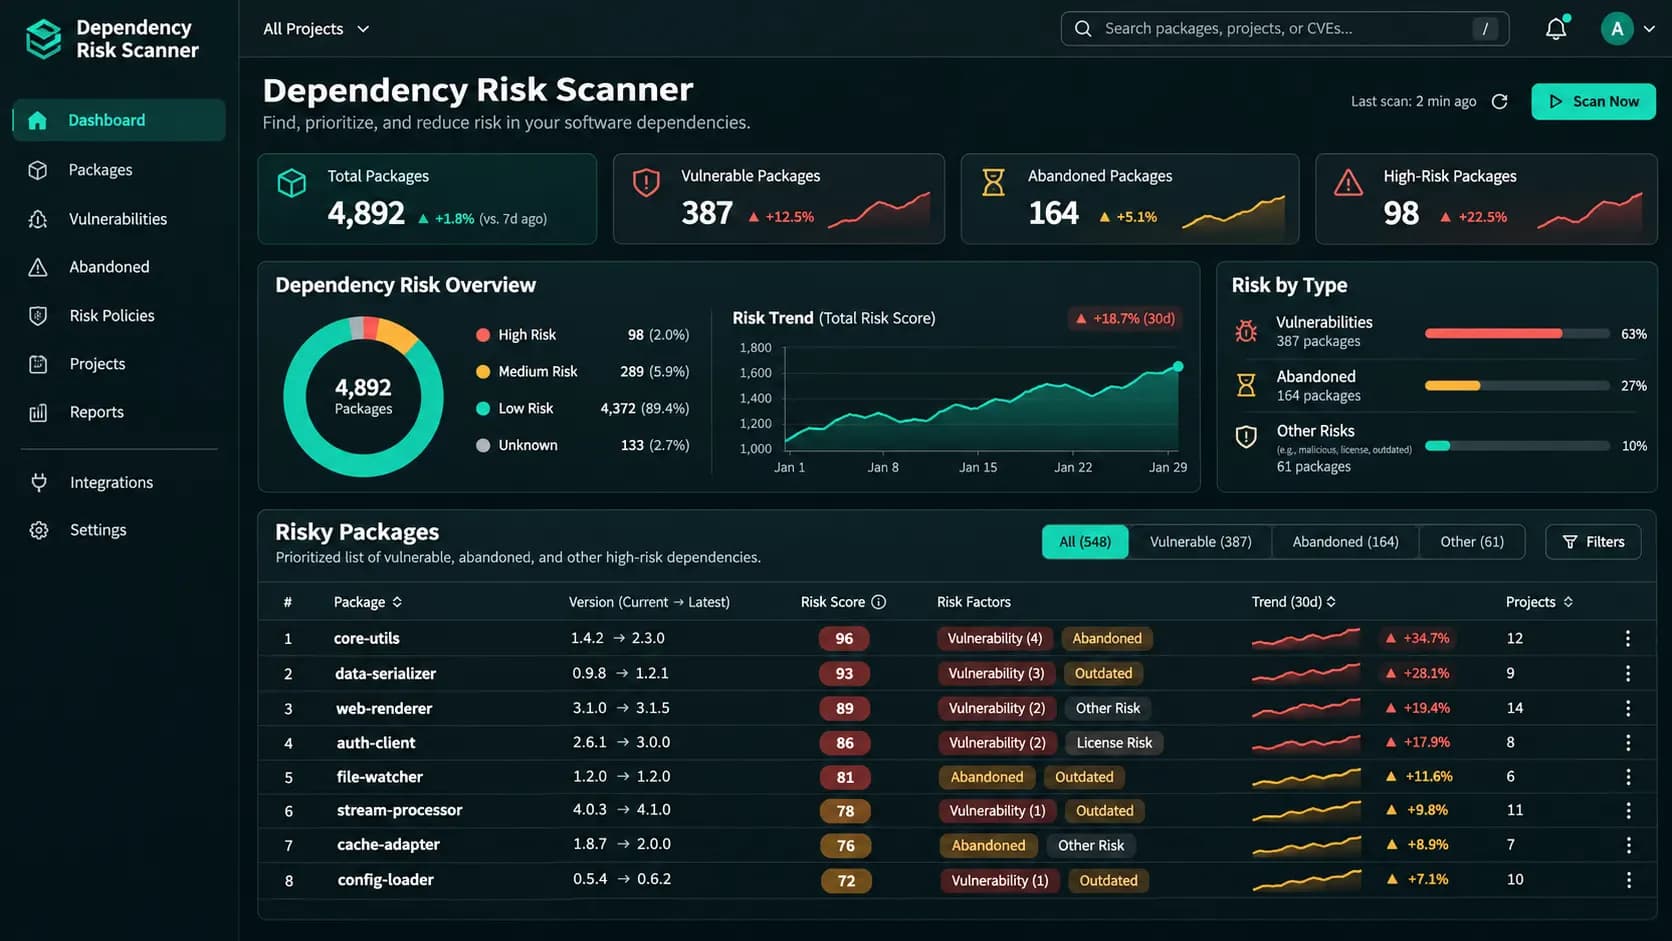
Prioritize vulnerable, abandoned, and risky packages
A supply-chain concept that continuously scans dependencies for CVEs, suspicious updates, abandoned packages, and license problems, prioritized by exploitability.
Some professional work is confidential. Public descriptions stay at a high level and omit customer data, internal systems, and unapproved screenshots.